OpenMAIC: Operating an Interactive Classroom Beyond the Demo
An operations-focused guide to OpenMAIC, covering providers, offline exports, persistence, render capacity, and security gates.
7 min
共 151 篇文章
An operations-focused guide to OpenMAIC, covering providers, offline exports, persistence, render capacity, and security gates.
Hermes v0.20.5 makes keyless models and web search easier to try, but durable agent operations still depend on evidence, permissions, and fallback design.
A practical look at Embabel, GOAP planning, typed actions, and operational checks for JVM teams.
A governance-oriented evaluation of local code graphs, benchmark limits, data boundaries, and PR review gates.
QUIC avoids some protocol ossification, but it changes observability, CPU, fallback, and edge operations.
Judge Cursor Origin by reviewability, merge state, source-of-truth rules, recovery, and ecosystem compatibility.
A practical operations guide to rendering quality, index backends, resource budgets, evaluation reproducibility, and rollback for visual retrieval.
A staged rollout and operations guide for Agent Reach, covering shell permissions, desktop/server differences, health checks, provenance, and failure handling.
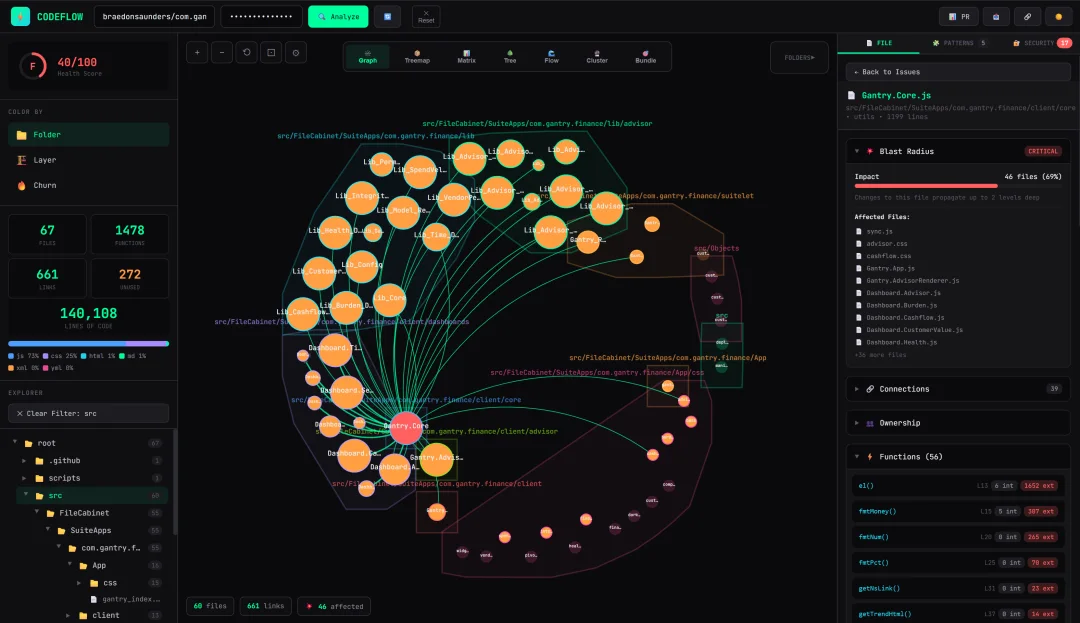
A factual review of browser-only repository analysis across public, private, and local modes, with focus on token scope, vendored dependencies, scanner limits, dynamic import blind spots, and a safe trial plan.
Simulation, evals, and guardrails can expand coverage, but teams still own policy, golden sets, false-positive budgets, privacy, auditability, and rollback.
An English security guide to OpenCode 1.x configuration, provider auth, model ID drift, Bun-installed plugins, and the boundary between official OpenCode and third-party harnesses like Oh My OpenCode / Oh My OpenAgent.
An operations and contract-focused review of Brnchost, with attention to traffic limits, abuse rules, billing uncertainty, and trial discipline.
Why a research agent should separate discovery, evidence retrieval, archive scope, and media processing instead of hiding everything behind one crawler.
A grounded operating view of what remains when AI handles PRD drafts, meeting cleanup, competitive research, and other repetitive product work.
A practical governance model for separating Obsidian notes, Hermes memory, session history, reusable SKILL.md files, review gates, permissions, and cron risk.
A governance reading of Google’s coding gap, rapid agent feedback, and the slower, more cautious path to AI Search.
Flowix turns a local Markdown workspace into a stable document boundary for agent work, with tighter context selection, inspectable outputs, BYOK controls, and clear adoption limits.
pdf-inspector shines when you use its CLI and APIs to inspect outputs, route only the needed pages to OCR, and handle confidence, encoding, and layout failures before they spread.
A security and governance review of Codux: codux-ssh, codux-db, read-only database profiles, P2P relay trust, remote hosts, and operational threat modeling.
An operations-focused guide to running Baidu Unlimited-OCR with clear GPU assumptions, serving choices, batch controls, observability, and validation gates.